

Configure SP-Initiated SSO for Procore in Microsoft Entra ID
Notes
- To complete setup, you will need to gather these parameters from your Microsoft Entra ID Enterprise application configuration: Single Sign On Issuer URL, Single Sign On Target URL (Optional for IdP-Initiated SSO), and Single Sign On x509 Certificate.
-
If you use Portfolio Financials and Capital Planning in Procore, contact your Procore point of contact or Contact Support for assistance with Microsoft Entra ID setup.
Background
Understanding Single Sign-On (SSO) terminology is key to configuring your integration correctly. Depending on your organization's setup, users can log in by starting at Procore (SP-initiated) or by clicking a tile in your corporate dashboard (IdP-initiated).
- To learn some key SSO Terms: Show/Hide
If your company uses Microsoft Entra ID to manage user logins to Procore, support is available for both Single Sign-On (SSO) authentication flows:
|
Authentication Flow |
How It Works |
Configuration |
|---|---|---|
|
SP-Initiated SSO |
Users navigate to the Procore login page, which redirects to Microsoft Entra ID for authentication before granting access. |
Follow the Steps below. |
|
IdP-Initiated SSO |
Users log into their Microsoft Entra ID portal and launch Procore directly by clicking the application tile. |
Things to Consider
- Required Permissions:
- You need both:
- Global Administrator rights to Microsoft Entra ID
- 'Admin' level permissions to Procore's Company level Admin tool.
- You need both:
- Prerequisites:
- Complete all the Preparation Phase steps outlined in Setup Guide: Microsoft Entra AD.
- Supported Product:
- Microsoft Entra ID
- Supported Authentication Protocol:
- Security Assertion Markup Language (SAML 2.0)
- Additional Information:
Steps
Important Requirement for Successful SSO
A user's Microsoft Entra ID primary email address must match their Procore login email address. To update a primary email address or alias to match Procore, follow the Microsoft documentation to Change a user name and email address.
Step 1: Add Procore as a New Enterprise Application in Entra ID
- Log in to the Microsoft Entra ID portal as a Global Administrator: https://entra.microsoft.com/auth/login/
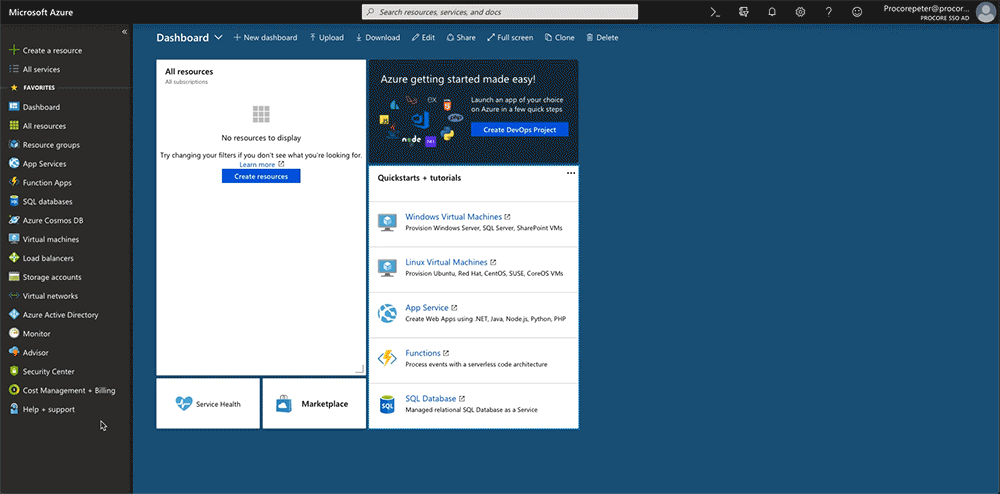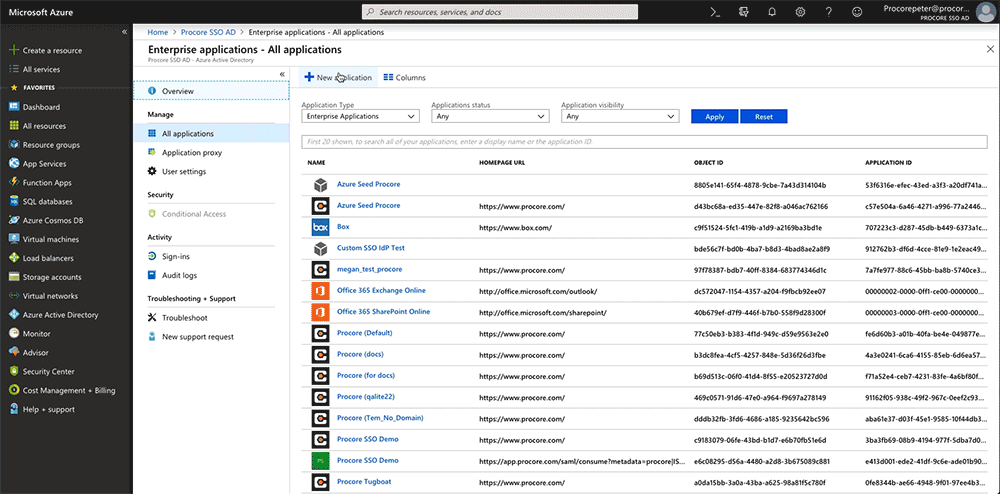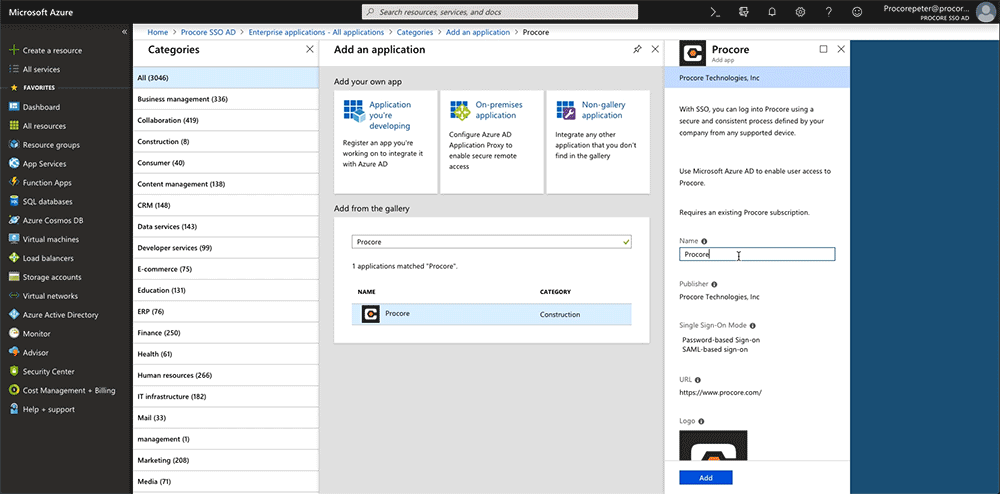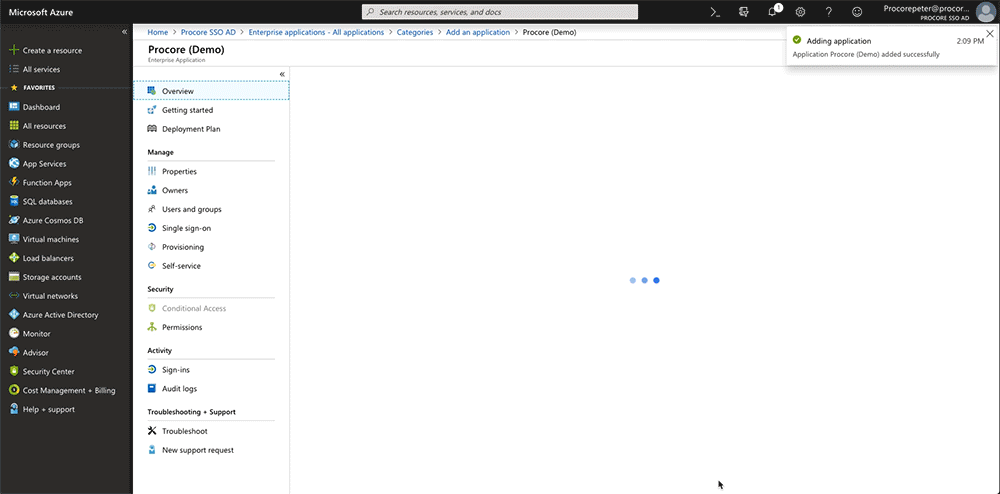
- Under Favorites, click Microsoft Entra ID.
- Under Manage, click Enterprise Applications.
- Click +New Application.
- Under Add from the Gallery, type the following in the Enter a Name box: Procore.
- Click the matching application named Procore.
This reveals a new pane. - In the Name box, type a name for your application.
Note: In the example above, we named our application: Procore (Demo) - Click Add.
A message appears to confirm that the application was added successfully. You should now be viewing your new Procore enterprise application's Overview page.
Step 2: Configure the Procore Enterprise Application's SSO Settings
- In the Overview page for your new enterprise application, under Manage, click Single Sign-On.
- In the Single Sign-on Mode page, click SAML.
This opens the Set Up Single Sign-On with SAML - Preview page. - Under Basic SAML Configuration, click Edit.
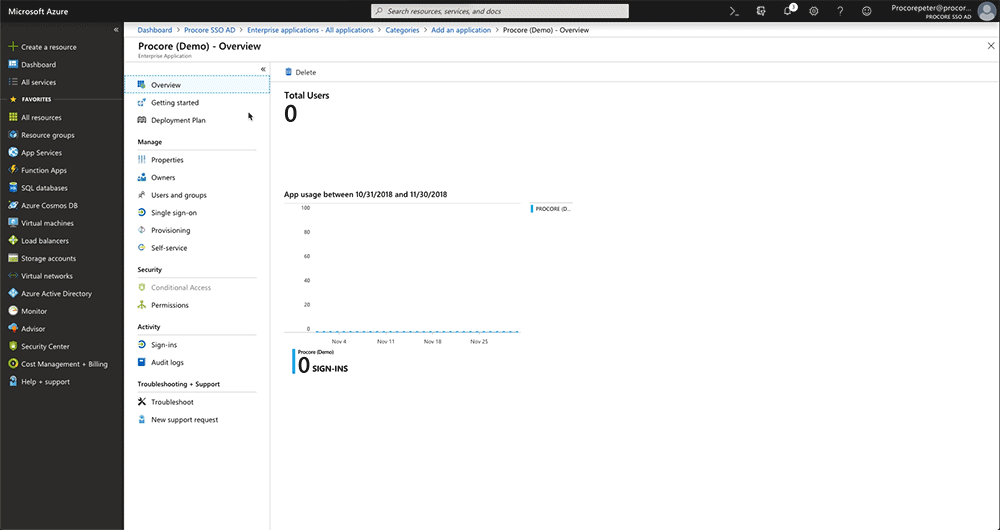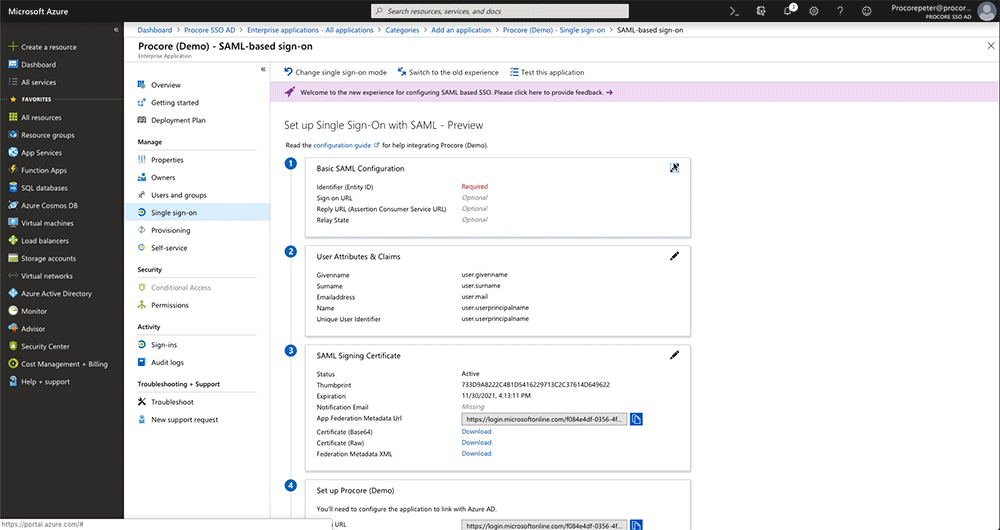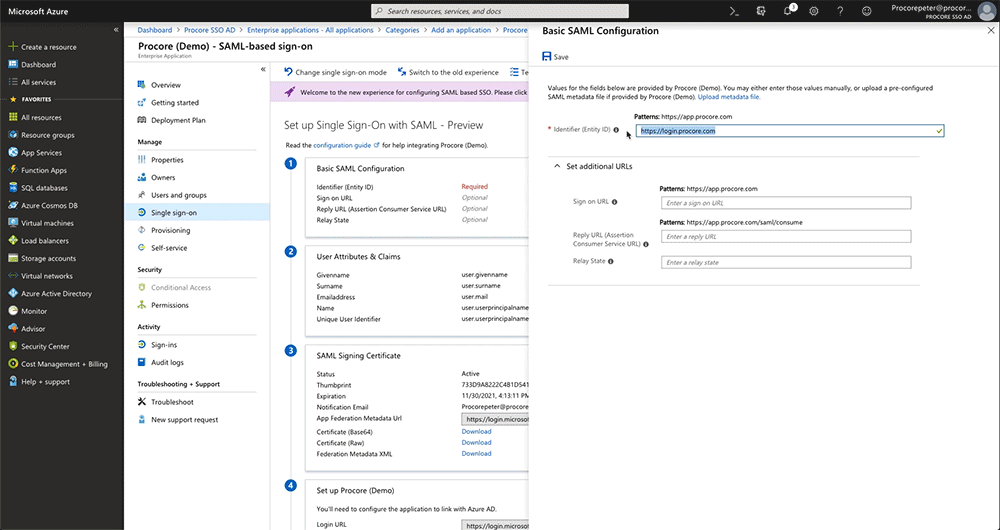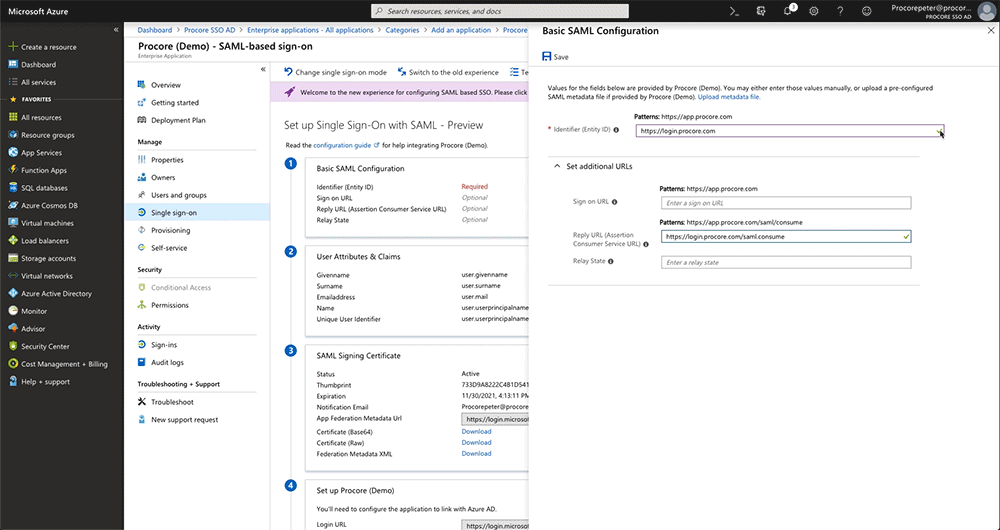
This opens the Basic SAML Configuration window. - Under the Basic SAML Configuration page, do the following:
- Identifier (Entity ID)
Change the value from:https://app.procore.comto:https://login.procore.com
Note: If you are using Portfolio Financials and Capital Planning, enter the following value instead:https://www.honestbuildings.com/pfcp/app/#!/loginOptional - Unique Entity ID
When configuring SSO for a single Procore instance, you should NOT check this box.
If your company licenses more than one Procore instance, and you want to configure unique Procore enterprise applications within your IdP tenant for each instance, you can by enabling Unique Entity ID. If enabled, you are still limited to one (1) enterprise application per Procore company instance.
Important: SSO for Procore targets users by email domain. An email domain can only be targeted once in all of Procore, so if you're considering setting up SSO with Unique Entity IDs across multiple Procore instances, remember that you can only target an email domain once, in a single instance.
To generate a Unique Entity ID for an enterprise application, check the Enable Unique Entity ID box in the Procore Admin tool's SSO configuration page for the Procore instance you want to specify on an enterprise application. Checking this box will generate a unique Entity ID URL in the field below, which you will then copy and paste into the appropriate Entity ID field in your IdP's configuration page.
Notes: You must save your configuration with the box checked to generate the Unique Entity ID. Enabling this feature does not impact user membership or access to a given instance. Access to a company in Procore is determined by a user's presence in the Directory tool, and their configured permissions within Procore. Auto-provisioning with SSO is not supported at this time.
- Sign On URL
Leave this field blank. You do NOT need to enter a value in this field. - Reply URL (Assertion Consumer Service URL)
Enter the following:https://login.procore.com/saml/consume
- Identifier (Entity ID)
- Click Save.
A message appears to confirm that your settings were saved successfully. - Click the 'x' to close the Basic SAML Configuration page.
- Under SAML Signing Certificate, click the Download link for the Certificate (Base64) file.
Notes:- This downloads a file named PublicCertificate.cer to your browser's specified download area.
- Open the file in a text editor and leave it open on your computer. Later, you will copy the code that appears between the ---BEGIN CERTIFICATE--- and ---END CERTIFICATE-- tags into Procore.
Step 3: Add the Entra ID Settings to Procore's Company Level Admin Tool
- Leave the Microsoft Entra ID page open as described in the previous step.
- Log into Procore using your Procore Administrator account.
- Navigate to the Company level Admin tool.
- Under Company Settings, click Single Sign On Configuration.
- Leave Procore's 'Single Sign On Configuration' page open.
- Go to the Microsoft Entra ID page that you left open.
- Under Set Up [Your Application Name], click View Step-by-Step Instructions.
This opens the Configure Sign-On page.
Copy this information from Microsoft Entra ID… Paste it into this field in Procore… SAML Entity ID
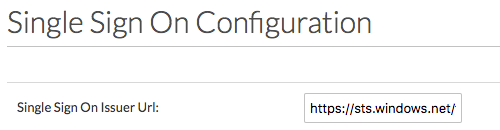
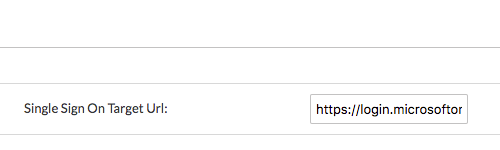
Copy the URL in this field from Microsoft Entra ID.Single Sign On Issuer URL
Paste the SAML Entity ID URL into the Single Sign On Issuer URL field.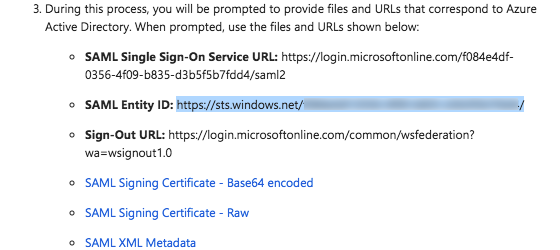
SAML Single Sign-On Service URL
Copy the URL in this field from Microsoft Entra ID.Single Sign On Target URL
Paste the SAML Single Sign-On Service URL into the Single Sign On Target URL field.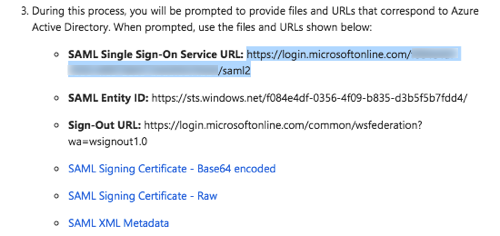
SAML XML Metadata
Download this file to your computer and open it in a text editor (i.e., Notepad or Text/Edit). Locate the certificate data that appears between the HTML start and end tags for the x509 certificate. Then copy the data. Do NOT copy the tags. This is depicted in the animated image above:Start Tag: <X509Data><X509Certificate>
End Tag: </X509Data></X509Certificate>
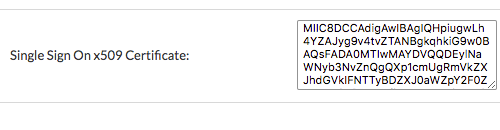
Single Sign On x509 Certificate
Paste the certificate data you copied into this field.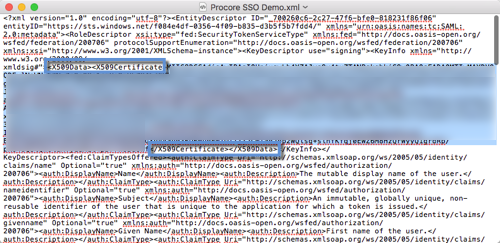
- On the 'Single Sign On Configuration' page in Procore, click Save Changes.
- Reach out to Procore Support or your company's Procore point of contact to request they configure the email domain(s) you'd like to target for SSO.
- After you receive confirmation that the SSO configuration is ready, mark the Enable Single Sign On checkbox on the 'Single Sign On Configuration' page.
- Select the Service Provider Forward option.
- Click Save Changes.
PROCORE SUPPORT: INTERNAL NOTE
Perform the steps below when notified by the Procore Administrator that the SSO configuration is complete:
- When notified by the Procore Administrator that the SSO configuration is complete, please be sure that the following fields are filled out:
- Single Sign On Issuer URL
- Single Sign On Target URL
- Single Sign On x509 Certificate
- Once confirmed, the domain(s) will need to be filled out by any employee on the @sup_sso ping. Please reach out to the @sup_sso team in #dept-cs-core.
- Once done, the client will be able to check the box for 'Enable Single Sign On'. When they do, they will see the following two options: ' Allow Password Login' (refers to IdP-Initiated) and 'Service Provider Forward' (refers to SP-initiated). We typically recommend they try 'Allow Password Login' first to test the connection.